# Roles
> Roles (PSROLEDEFN) are named bundles of permission lists. Users get roles, not permission lists directly.
---
Site [llms.txt](/llms.txt)
---
## Roles
**URL:** `/roles`
Roles (PSROLEDEFN) are named bundles of permission lists. Users get roles, not permission lists directly.
Walkthrough: Exploring Roles in psLens
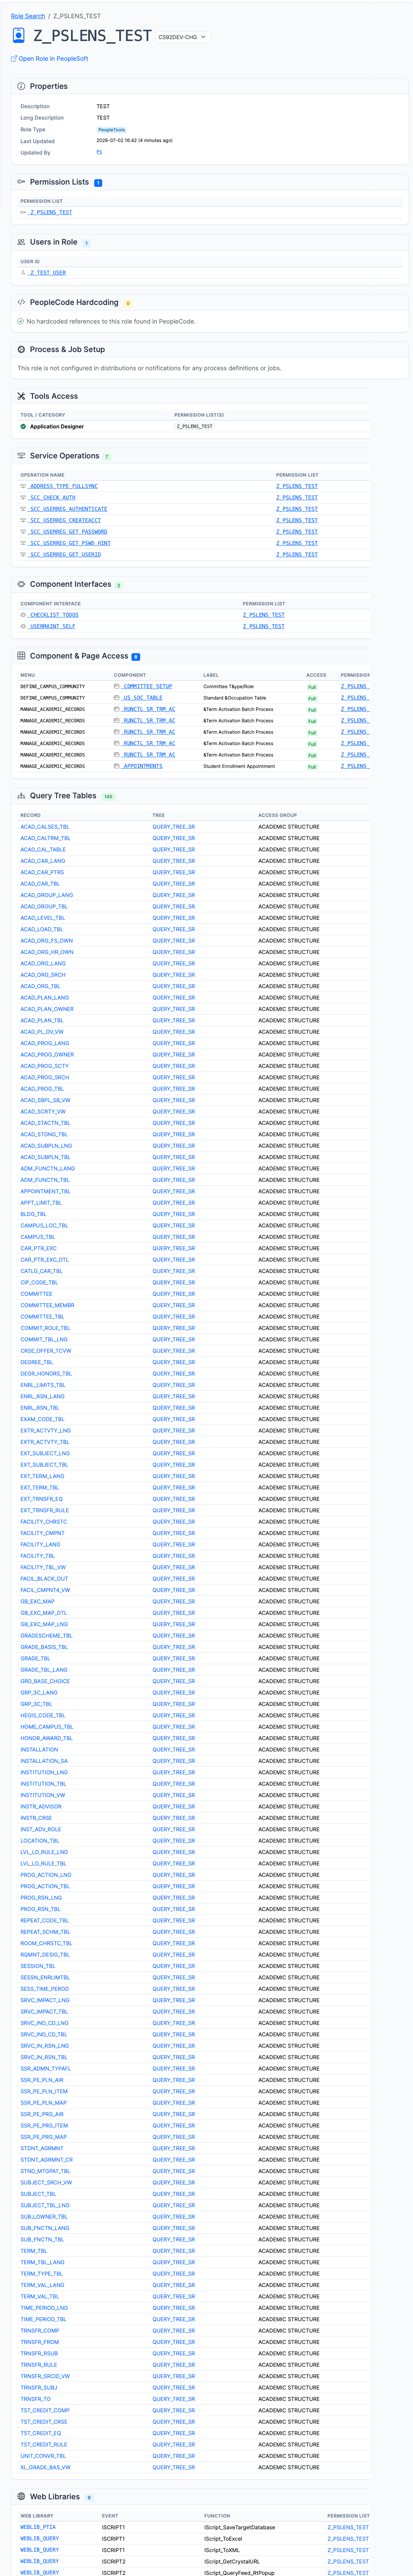
Role detail page with the permission lists, users, and aggregate access needed to understand what the role actually grants
### What You Can Do
- **View Included Permission Lists:** See the list of permission lists assigned to the role.
- **View Assigned Users:** See which users are assigned this role.
- **Compare Roles (Cross-Database Diff Tool):** Compare two role definitions across databases (or within the same environment) at `/roles/compare` (accessible from the **Security > Compare Roles** sidebar menu or search header). Diffs assigned permission lists, assigned users (with dynamic assignment flags), effective aggregate page/menu, web library, service operation, CI, process group, and query access groups, plus process notifications/distributions. Features continuous-scroll layout with sticky navigation, summary metrics, and Markdown export.
- **View Authorizations:** See the aggregated Tools Access, Service Operations, Component Interfaces, Component & Page Access, Query Tree Tables, and Web Libraries granted by the permission lists assigned to the role.
- **Metadata Inspection:** See the role's description and last modified information.
### When It's Useful
- Understanding what an unfamiliar role grants.
- Checking whether a role contains permission lists that are unexpectedly broad.
- Finding all users who have a particular role.